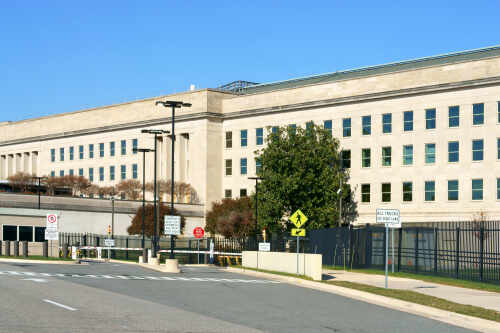
The Pentagon just froze tougher cyber rules for defense contractors, raising big questions about security, small business survival, and government red tape.
Story Snapshot
- The Department of War suspended CMMC Phase 2, stopping third-party cyber certifications that were set for November 10, 2026.
- Officials say the pause protects small contractors from crushing costs while keeping core security rules in place.
- A new 60-day CMMC Reform Task Force will review the program and recommend changes to cut bureaucracy.
- Contractors still must follow existing cyber standards, but the government cannot require outside certifications during the suspension.
Pentagon Freezes Phase 2 Cyber Rules To Cut Red Tape
The Department of War announced that the planned November 10, 2026 transition to Cybersecurity Maturity Model Certification Phase 2 is suspended, stopping new third-party certification requirements before they take effect. Phase 1, which relies on contractor self-assessments to show how they protect controlled unclassified information, remains in place and enforced. Officials framed the move as part of a broader acquisition strategy that favors speed, lower barriers for new suppliers, and “scalable, resilient cybersecurity measures” instead of heavy paperwork.
Department of War Chief Information Officer Kirsten Davies said the department is suspending CMMC Phase 2 requirements and starting a 60-day study of the program to align it with Secretary Pete Hegseth’s acquisition initiatives. A formal directive to program managers now bars them from requiring CMMC Level 2 certifications by outside assessment organizations or Level 3 government-led assessments in new procurements during the suspension. Only Level 1 self-assessments or Level 2 self-assessments may be used in contract documents, marking an immediate halt to expanded third-party cyber checks.
Small Businesses Win A Breather, But Compliance Still Counts
The Small Business Administration praised the suspension, warning that planned Phase 2 rules and third-party audits were pushing smaller firms out of defense work as costs climbed toward hundreds of thousands of dollars per company. With over 100,000 small businesses touched by CMMC, the agency argued that high compliance costs and complex audits threatened innovation and a broad defense supply base. By stopping Phase 2, the Department of War aims to keep strong cybersecurity while cutting rules that block new and non-traditional suppliers from competing.
At the same time, officials stressed that cybersecurity obligations have not gone away, only the certification mechanism. Existing rules tied to the Defense Federal Acquisition Regulation Supplement and National Institute of Standards and Technology Special Publication 800-171 still require contractors to protect defense data and prove that protection when the government asks. Analysts explain that what is under review is “who checks your homework, and how often,” not the standard itself. For now, the Pentagon will rely on self-assessments and selected government-led reviews instead of full third-party audits.
Reform Task Force To Rethink Phase 2 And Future Enforcement
The suspension launches a new CMMC Reform Task Force with orders to deliver recommendations within 60 days to the Department of War Chief Information Officer. The review will look at how the program can support the Warfighting Acquisition Strategy, which focuses on fast delivery of capability and lower barriers for small and non-traditional businesses. Government and industry briefings say the goal is to replace “burdensome compliance regimes” with approaches that are easier to scale, especially for smaller firms that lack large compliance teams.
However, there is little public detail yet on who sits on the task force, how it will measure program success, or what changes it might propose. Earlier Government Accountability Office work shows that most major Defense Department information technology programs suffer serious schedule delays and cost changes, hinting that long cyber rule timelines and complex enforcement can strain agencies and contractors alike. Conservative observers see this pause as a chance to demand simpler, clearer rules that protect national security without crushing private sector partners under never-ending audits and shifting checklists.
What The Suspension Means For Contractors And Patriots
For defense contractors, the immediate impact is that upcoming solicitations and contract documents cannot demand CMMC Level 2 certifications by outside assessment organizations or advanced government assessments while the suspension is in place. Companies still must perform and document self-assessments at Level 1 or Level 2 and be ready for government reviews, but the costly rush to secure third-party certifications before November 10, 2026 is on hold. Industry analysts warn that firms should treat this as breathing room, not an excuse to weaken cyber defenses, because core data protection rules still apply and can be enforced through other channels.
For constitutional conservatives, the story highlights a familiar pattern: Washington builds complex programs, overreaches with mandates, then scrambles to fix the mess when small businesses start walking away. The suspension of Phase 2 shows growing recognition that heavy-handed certification schemes can shrink the defense industrial base and slow delivery of tools our warfighters need, all while doing little to stop real cyber threats. The next 60 days will decide whether the Pentagon turns this pause into a lasting shift toward leaner, more targeted cybersecurity that respects both national security and the freedom of American enterprise.
Sources:
insidedefense.com, nextgov.com, csoonline.com, digital.nationaldefensemagazine.org, pillsburylaw.com, dodcio.defense.gov, linkedin.com